An overseas proxy IP failing isn't usually a single-cause problem. Troubleshoot in order of "local network connection, proxy authentication, proxy protocol, target site response" — and locate the specific failure layer by swapping test addresses, inspecting status codes, and comparing against direct connections.
When an overseas proxy IP is configured but requests still fail, common symptoms include can't connect, authentication failure, request timeout, frequent disconnects, and error pages returned by the target site. Don't swap proxies directly — judge which layer the problem lives in first to cut wasted troubleshooting.
Why Troubleshoot Overseas Proxy IP Failures Layer by Layer?
Proxy IP requests pass through multiple stages — an anomaly at any stage can present as "proxy failed."
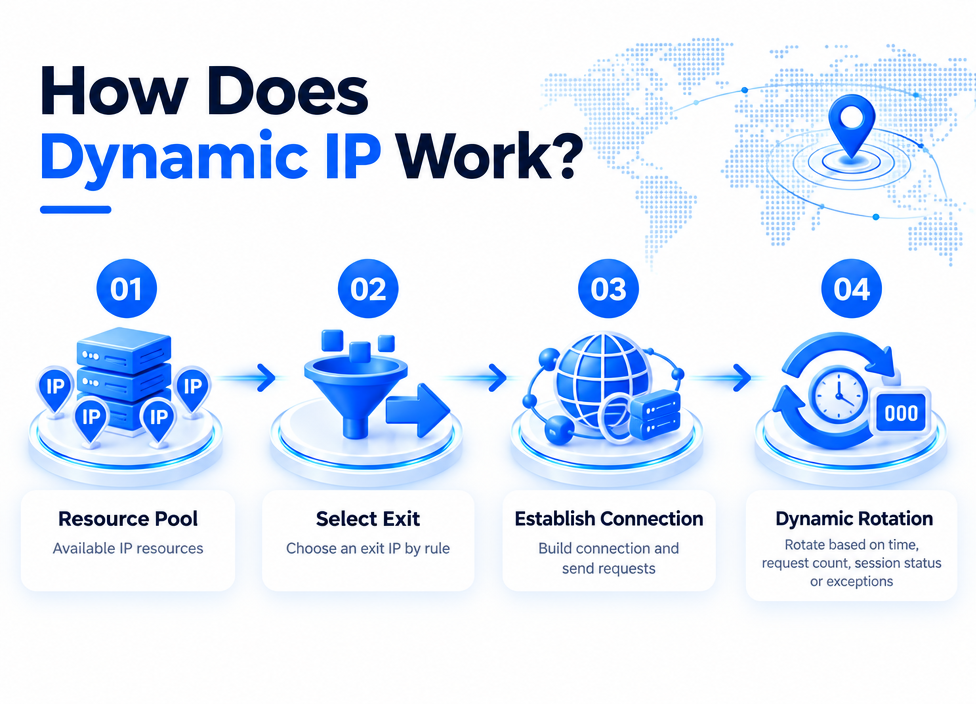
A complete request roughly follows this path:
- Local device or server connects to the proxy address.
- Proxy service validates account, password, or allowlist.
- Proxy service establishes connection to the target site.
- Target site receives the request and returns a response.
- Client parses the response and continues downstream processing.
Judge the problem scope by symptoms first:
| Symptom | Priority Check |
|---|---|
| Proxy address and port can't connect | Local network, port, address validity |
| 401 or 407 returned | Username, password, authentication method |
| Long no-response after connection established | Network latency, line quality, target site response |
| 403 or 429 returned | Target site policy, request frequency, request signature |
| Only HTTPS fails | Proxy protocol, TLS connection, or certificate handling |
| Some regions work, others fail | Exit region, target site regional restrictions |
| Requests occasionally succeed, occasionally time out | Connection reuse, node stability, concurrency or timeout settings |
How to Confirm Whether the Problem Is Local Network or Proxy Address?
If you can't even connect to the proxy server, check address, port, and local network first.
Troubleshoot in this order:
- Verify proxy address and port
Check for stray spaces, incorrect port, and whether domain and port belong to the same configuration set. - Confirm protocol type
HTTP proxy, HTTPS proxy, and SOCKS5 proxy configure differently. Using a SOCKS5 address as an HTTP proxy may cause connection failures or request anomalies. - Test domain resolution
If the proxy uses a domain connection, confirm the local environment can resolve it. Abnormal DNS configuration on the server can also create a false appearance of "proxy unavailable." - Check exit network restrictions
Enterprise networks, firewalls, security groups, or cloud server policies may restrict outbound connections on non-standard ports. Test other normal external services in the same environment to judge whether it's an overall outbound issue. - Reduce connection complexity
Test with single requests, low concurrency, and longer timeouts first — don't start by enabling connection pools, concurrent requests, and auto-retry.
In a command-line environment, baseline testing can look like:
curl -v -x http://username:password@proxy_host:port https://target_domainUse placeholders in place of real credentials during testing — avoid writing accounts and passwords into scripts, logs, or command history.
What to Check When 401 or 407 Returns?
401 and 407 usually point to authentication information or method problems — not the target site itself.
Focus on:
- Whether username is complete; whether prefix, region, or session parameters were accidentally stripped
- Whether the password contains special characters, and whether they're correctly encoded
- Whether the client sends authentication info to the proxy layer, not mistakenly to the target site
- Whether credential-based auth or IP allowlist auth is configured
- Whether the current exit IP is still in the allowlist
- Whether the account is expired, out of balance, or at concurrency limit
- Whether HTTP proxy and SOCKS5 proxy authentication fields are configured correctly
- Whether proxy auth info is lost after a redirect
If the same credentials behave differently across clients, check the client's proxy configuration format first — don't immediately conclude the account is invalid.
What If Only HTTPS Requests Fail?
When only HTTPS fails, focus on proxy protocol, TLS connection, and client certificate handling.
Run two comparisons first:
- Access a simple HTTP address through the proxy
- Access a simple HTTPS address through the proxy
If HTTP works but HTTPS fails, possible causes:
- The client doesn't support the current proxy's HTTPS tunneling method.
- The proxy address's protocol prefix is misconfigured.
- TLS version or cipher suite is incompatible.
- The client's certificate validation is too strict.
- Middle network devices intercept or restrict TLS connections.
- The target site requires more complete request signatures that simple test tools can't handshake.
Use standard clients and default certificate validation during troubleshooting — don't disable certificate validation just to make requests succeed. If it only works after disabling validation, the real problem isn't solved.
How to Judge When the Target Site Returns 403 or 429?
403 and 429 mean the request already reached the target site — the focus shifts from "can it connect to the proxy" to "how is the target site handling the request."
Judge from these angles:
- 403: may relate to exit region, request headers, access permissions, session state, or request signatures.
- 429: usually relates to too many requests per unit time, excessive concurrency, or overly aggressive retries.
- 503: may be the target site temporarily unavailable, or a middle service unable to fetch a response in time.
Run three comparisons:
- Same proxy accessing different target sites.
- Different proxies accessing the same target site.
- Access the same target site again after reducing frequency and concurrency.
If only one target site returns 403 while others are normal, the proxy chain may not be the problem — check that target's access rules and request requirements first. If 429 drops noticeably after reducing concurrency, adjust the request rhythm instead of simply adding more retries.
What If Requests Frequently Time Out or Drop?
Split timeouts into connection timeout, read timeout, and target response timeout — they call for different handling.
- Connection timeout: proxy address unreachable, excessive line latency, or restricted ports.
- Read timeout: connection established, but proxy or target site slow to return data.
- Target response timeout: proxy works fine, but target site takes long to process.
Troubleshooting suggestions:
- Set connection timeout and read timeout separately.
- Lower concurrency first — observe per-request time.
- Disable overly aggressive connection-reuse settings.
- Set bounded exponential backoff retries for failed requests.
- Log proxy address, target domain, status code, time cost, and error type.
- Compare response times across different exit regions.
- Check whether oversized request body or response content extends client wait time.
Retry doesn't solve all timeout problems. If failures happen at the same time point every time, it's more likely a fixed timeout configuration or target response issue.
What's a Complete Troubleshooting Sequence?
The most effective sequence moves from the lowest-layer connection step by step toward the target site.
Execute in this order:
- Confirm proxy address, port, and protocol.
- Test whether local can connect to the proxy port.
- Use a single request to validate authentication.
- Access a simple HTTP and HTTPS address first.
- Then access the actual target site.
- Log status codes, response times, and error information.
- Lower concurrency to rule out frequency and connection-reuse effects.
- Swap exit regions to judge whether regional differences exist.
- Re-test with another client or standard tool.
- Only swap configuration or submit for service-side investigation after the fault scope is clear.
Keep a minimal test script containing only proxy address, a single target address, and baseline timeout settings. Retries, caches, async tasks, and multi-threading in complex business scripts easily mask real failures.
FAQ
Q: The proxy IP connects but target site requests keep timing out — does that mean the proxy failed?
Not necessarily. A successful connection only proves the local-to-proxy chain is basically usable. Target site timeouts may also come from exit region, target response speed, request concurrency, or read-timeout configuration. Access other target sites first, then lower concurrency and log connection time and read time — separate proxy chain issues from target response issues.
Q: Why does the same proxy work locally but not on the server?
The two environments may differ in DNS, exit network, firewall, security groups, and system time. Servers may also restrict non-standard ports or alter TLS configuration. Run the same minimal test request in both environments and compare resolution results, connection time, error codes, and outbound policy.
Q: Proxy credentials are verified correct but 407 still returns — what to do?
Keep checking authentication type, username format, special-character encoding, and allowlist configuration. Some services require writing region, session, or line parameters into the username field — missing fields may also be read as auth failure. Also confirm the client isn't losing proxy auth after redirects.
Q: On 403, should you swap proxies first or check the request first?
Check request frequency, request headers, session state, and target site access rules first — then do bounded proxy switching. If other target sites are normal and only one returns 403, the problem more likely sits in target site policy, not an entirely unusable proxy.
Q: Why do testing tools succeed but the business program fails?
Testing tools usually send a single simple request; business programs may use concurrency, connection pools, redirects, complex request headers, or auto-retry. Roll the business program back to single-request, low-concurrency, default-timeout state first, then restore configuration item by item to isolate the specific influencing factor.
Q: When troubleshooting proxy failures, which logs are most useful?
Log at minimum request time, proxy address or node identifier, target domain, protocol, status code, connection time, read time, and client error type. Mask account passwords, full request headers, and sensitive business parameters before saving — avoid letting logs themselves introduce security risks.